
When I run the "wireshark" in ubuntu 20.04. I got the error message and can't execute wireshark successfully. I ALWAYS GOT THIS ERROR
qt.qpa.plugin: Could not find the Qt platform plugin "xcb" in ""
This application failed to start because no Qt platform plugin could be initialized. Reinstalling the application may fix this problem.
I do the searching I found many solutions. BUT that didn't work for me. I have installed every application they mentioned.
horace papa 發表在
痞客邦
留言(0)
人氣()
tables:
==================
1)a table is something that allows you to process packets in specific ways
2)default table is the "filter" table,these "tables" have "chains" attached to them
|
horace papa 發表在
痞客邦
留言(0)
人氣()
Automatic Variables
Suppose you are writing a pattern rule to compile a ‘.c’ file into a ‘.o’ file: how do you write the ‘cc’ command so that it operates on the right source file name? You cannot write the name in the recipe, because the name is different each time the implicit rule is applied.
What you do is use a special feature of make, the automatic variables. These variables have values computed afresh for each rule that is executed, based on the target and prerequisites of the rule. In this example, you would use ‘$@’ for the object file name and ‘$<’ for the source file name.
It’s very important that you recognize the limited scope in which automatic variable values are available: they only have values within the recipe. In particular, you cannot use them anywhere within the target list of a rule; they have no value there and will expand to the empty string. Also, they cannot be accessed directly within the prerequisite list of a rule. A common mistake is attempting to use $@ within the prerequisites list; this will not work. However, there is a special feature of GNU make, secondary expansion (see Secondary Expansion), which will allow automatic variable values to be used in prerequisite lists.
Here is a table of automatic variables:
horace papa 發表在
痞客邦
留言(0)
人氣()
if you are suffer the problem
sudo apt-get install teams
Reading package lists... Done
Building dependency tree
Reading state information... Done
horace papa 發表在
痞客邦
留言(0)
人氣()
error: dereferencing pointer to incomplete type 'RSA {aka struct rsa_st}' if (BN_num_bits(key->e) > 64) ^~ scripts/Makefile.host:134: recipe for target 'tools/lib/rsa/rsa-sign.o' failed
Solution: http://git.lede-project.org/70b104f please fix by this patch.
diff --git a/tools/mkimage/patches/210-openssl-1.1.x-compat.patch b/tools/mkimage/patches/210-openssl-1.1.x-compat.patch
new file mode 100644 (file)
index 0000000..fa7c99f
horace papa 發表在
痞客邦
留言(0)
人氣()

the librt.so.1 share liberary missing after update or remove some ubuntu application, the below is a way to rescuse ubuntu boot up failure issue.
1.Boot from installation medium(live cd)
2.Mount your problematic Ubuntu root filesystem with file manager by clicking on the drive icon in the Devices section
If unsure which partition to mount then check it with Disks (gnome-disks) utility and mount it from here:
4. go to download the missing liberaries by here (debian packet searchig website) or http://http.us.debian.org/debian/pool/main/g/glibc/
horace papa 發表在
痞客邦
留言(0)
人氣()
horace papa 發表在
痞客邦
留言(0)
人氣()
https://www.shellcheck.net/
horace papa 發表在
痞客邦
留言(0)
人氣()
horace papa 發表在
痞客邦
留言(0)
人氣()
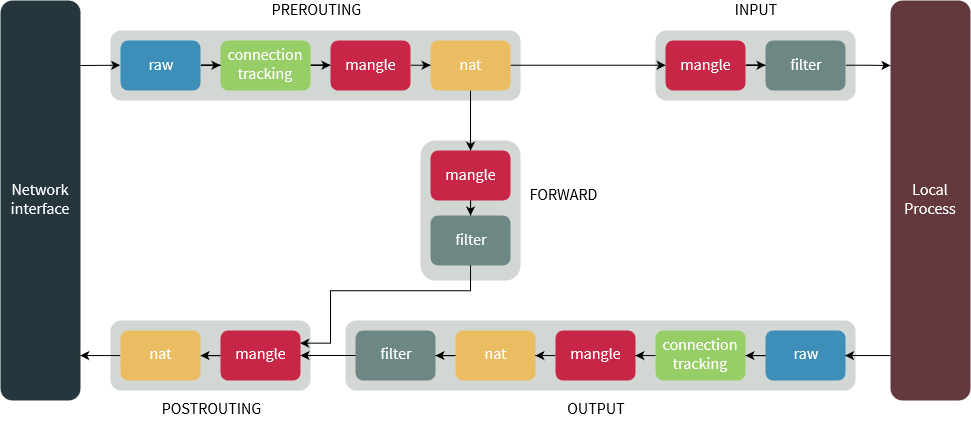
https://www.booleanworld.com/depth-guide-iptables-linux-firewall/
a very good doc for understanding iptables.
he Linux kernel comes with a packet filtering framework named netfilter. It allows you to allow, drop and modify traffic leaving in and out of a system. A tool, iptables builds upon this functionality to provide a powerful firewall, which you can configure by adding rules. In addition, other programs such as fail2ban also use iptables to block attackers.
In this article, we’re going to take a look at how iptables works. We’re also going to look at a few examples, which will help you write your own rules.
horace papa 發表在
痞客邦
留言(0)
人氣()
First of all let me give you a brief on the insides of Ethernet MAC.
We have a MAC module which interacts with Physical layer and we have DMA which interacts with memory. So the Ethernet frame flow is like this
Transmit:
Memory-->DMA-->MAC-->Physical Layer
Receive:
horace papa 發表在
痞客邦
留言(0)
人氣()

1) run "tmux"
2)"tmux ls" list all the tmux session
3) change tmux prefix key by editing ~/.tmux.conf
#change prefix key from C-b to C-x
unbind C-b
horace papa 發表在
痞客邦
留言(0)
人氣()


